-
Shop
- Advanced Technologies
- AI Career Advantage Collection
- AI Skills Mastery 2026 Collection
- Bathroom
- Best-Sellers
- Car Accessories
- Dating & Social Skills
- Digital Resources
- AI Skills
- Beauty
- Car Buying & Ownership
- Cozy Feast Collection
- Electronics & Technology
- Emotional Intelligence
- Financial Education
- Home Styling & Organization
- Mindset
- Online Business
- Parenting & Child Development
- Personal Style & Fashion
- Pet Lifestyle & Wellness
- Positive Thinking
- Self Confidence
- Sleep Improvement
- Smart Life with AI
- Stress Management & Relaxation
- Wellness
- Yoga & Fitness
- Yoga & Mind-Body Practices
- Education & Learning
- Family & Parenting
- Fashion
- Furniture
- Gadgets
- Health & Beauty
- Health & Wellness
- Home & Garden
- Home Electronics
- Jewelry
- Kids & Babies
- Kitchen
- Lighting
- Online Business for Beginners
- Patio, Lawn & Garden
- Personal Growth
- Pet Care
- Pet Supplies
- Pets
- Shoes
- Smart Home Living Guides
- Sport & Outdoors
- Stress Relief & Relaxation
- TikTok Growth & Monetization Mastery
- Travel
- Travel Planning
- Wealth
- Wealth Building
- Budgeting & Saving
- Cryptocurrency Investing
- Debt Management
- Entrepreneurship & Business Growth
- Family Finance & Budgeting
- Financial Independence
- Financial Mindset & Psychology
- Financial Planning
- Frugal Living & Expense Hacks
- Goal Setting
- High-Income Skills
- Investing Basics
- Leadership
- Motivation
- Networking & Mentorship
- Passive Income Strategies
- Real Estate Investing
- Side Hustles
- Stock Market Investing
- Popular
- Best deals
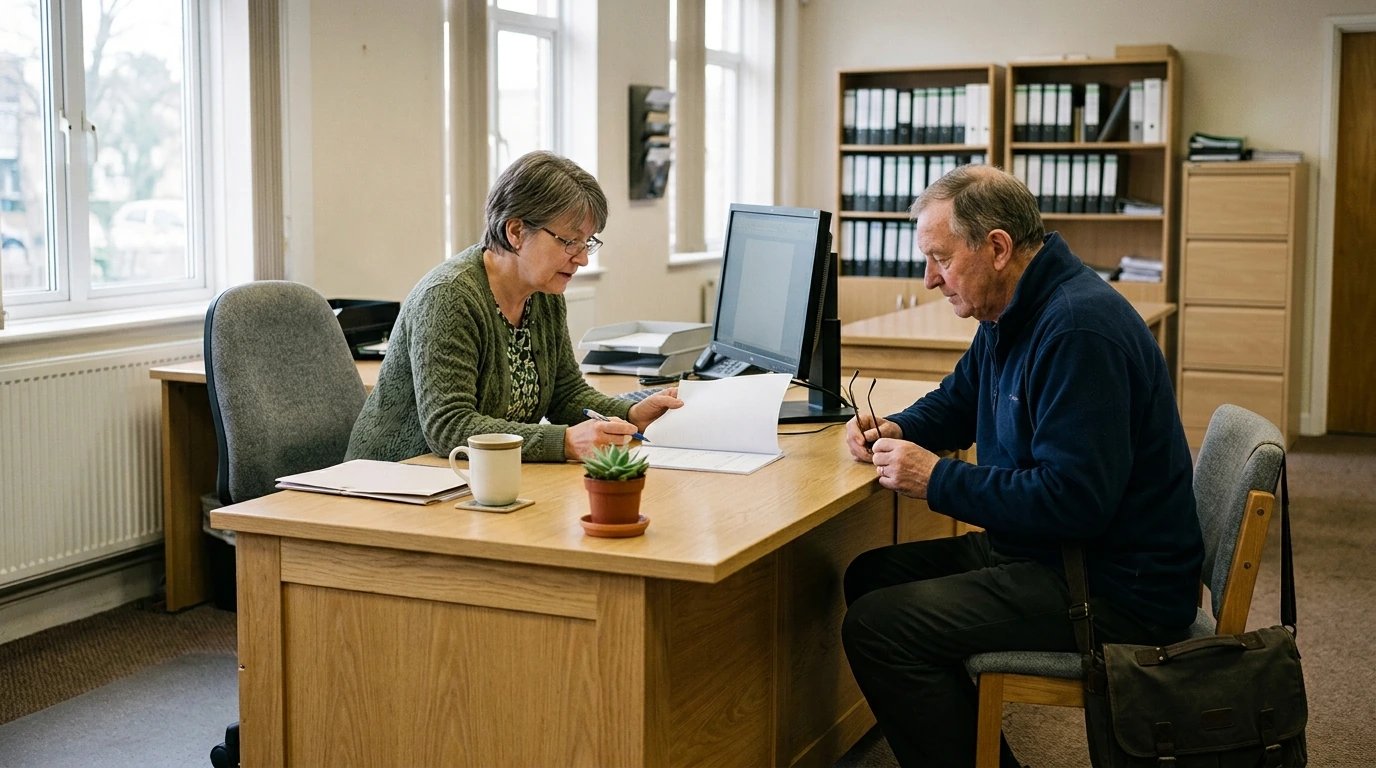
A Practical Guide to AI in Government Services
25% off on product page · save $2.66
A Practical Guide to AI in Government Services
Where AI Can Help—and Where Caution Comes First
AI assistance is not the same as AI decision-making. A tool that drafts a routine reply for an employee to check and approve plays a different role from one that determines whether a resident qualifies for a benefit. The latter can directly affect someone’s access to essential services and calls for substantially stronger oversight.
Useful starting points include sorting incoming requests, summarizing lengthy records for staff review, flagging possible maintenance needs, and locating information in approved policy documents. Each use still needs boundaries. A summary may omit a decisive detail, while a request-routing tool may fail to recognize an urgent case. Staff must be able to inspect the underlying information and correct the result.
Residents also need a way to understand what happened, report a problem, and seek correction where appropriate. A process that moves faster but leaves people unable to challenge an error is not necessarily an improvement.
Distinguish Assistance From Decision-Making
The table below is a starting point for discussing benefits and safeguards—not a substitute for an agency-specific risk assessment. Data sensitivity, potential harm, and the ease of correcting mistakes should shape whether a use case proceeds at all.
Practical AI uses and the checks they require
| Use case | Potential benefit | Essential safeguard |
|---|---|---|
| Drafting routine correspondence | Reduces time spent on first drafts | Staff verify facts and approve every response |
| Searching approved policy documents | Helps staff locate relevant guidance | Answers cite current source documents |
| Routing service requests | Directs cases to the appropriate team | Staff can correct misrouted or urgent cases |
| Supporting eligibility reviews | Helps organize evidence for reviewers | Authorized people make decisions and provide appeal paths |
Even a seemingly routine task can become high risk when it involves sensitive records or delays urgent help. Before adoption, identify who may be affected, how an error would be detected, and how quickly it could be fixed.
Featured in this guide
AI in Government Services Guide | Practical AI in Government Services for Public Sector Innovation, Automation & Smart Decision-Making
Match the Safeguard to the Task
Use cases differ in sensitivity and consequence. This comparison is a discussion aid, not a substitute for an agency-specific risk assessment.
| Use case | Potential benefit | Essential safeguard |
|---|---|---|
| Drafting routine correspondence | Less time spent on first drafts | Staff verify facts and approve responses |
| Searching approved policy documents | Faster access to relevant guidance | Answers point to current source documents |
| Routing service requests | Cases reach the appropriate team | Staff can correct misrouted or urgent cases |
| Supporting eligibility reviews | Evidence is easier for reviewers to organize | Authorized people decide, with a path to appeal |
Even routine work can become high risk when it involves sensitive records or delays urgent help. Consider both the likely error and how quickly it could be found and fixed.
Make the Pilot Small Enough to Learn From
Choose one bounded workflow with a clear owner and a baseline for comparison. Searching a limited set of approved guidance, for example, may be easier to evaluate than changing an entire case-management process. Keep the existing workflow available during assessment.
Define success before deployment. Track processing time and errors alongside staff workload, accessibility, and resident outcomes. Test incomplete records, conflicting documents, unusual requests, and language or accessibility needs—not just straightforward examples.
Record failures and set a review date. Decide in advance what evidence would justify expanding, revising, or ending the pilot.
Build Accountability Into Daily Work
Before staff enter information into a tool, establish what data it receives, whether personal information is necessary, who has access, and what retention and vendor terms apply. Bring security, privacy, legal, and procurement teams into the review under applicable requirements.
Name the people responsible for approving outputs, recording errors, handling complaints, and escalating consequential cases. Staff instructions should distinguish permitted assistance from uses that are prohibited or require a person to decide. Training should address inaccurate outputs, secure handling, and automation bias—the tendency to accept a tool’s answer too readily.
The NIST AI Risk Management Framework and the U.S. Government Accountability Office AI Accountability Framework can help structure questions about risk and accountability throughout a system’s life cycle. Revisit fairness, transparency, security, and performance after launch, not only before it.
Turn the Work Into a Decision
Identify one service problem, assess the risks, set safeguards, run a bounded pilot, and compare its outcomes with the existing process. Document why the use case was chosen and what evidence supports the next decision. That record helps an agency explain both progress and course corrections.
The featured AI in Government Services Guide is a planning resource focused on public-sector innovation, automation, and decision support. It does not replace legal, procurement, privacy, or security review.
Compare related options such as Smart Tips to Keep Your Phone Battery Healthy: Essential Guide for Maximum Battery Life to match features, dimensions, and use case before choosing.
FAQ
What AI service does the US government use?
There is no single AI service used across the entire US government. Agencies evaluate and use different tools for specific purposes under their own requirements and applicable federal guidance.
Which 3 jobs will survive AI?
No credible list can guarantee that exactly three jobs will survive AI. Roles may change as tools evolve; work requiring human accountability, complex judgment, and direct care is less easily reduced to automated tasks.
What is the 30% rule for AI?
There is no universally recognized “30% rule” governing AI in government services. Ask which policy, metric, or organization the phrase refers to before treating it as an official threshold.
What is the government version of ChatGPT?
There is no universal, government-wide version of ChatGPT. Some agencies may offer approved internal generative AI tools, but availability and permitted uses vary by agency.
See if AI in Government Services Guide | Practical AI in Government Services for Public Sector Innovation, Automation & Smart Decision-Making fits your setup
Content Stalled? A Practical Reset for Creators
Sep 26, 2026



Leave a comment